Security Shield: website security check
What the scanner checks in eight areas, how to read the A–F rating, why to verify the domain, what auto-fix can do, and what the check does not replace.
Security Shield — a website security check service. It looks at the site from the outside, as an attacker would, and shows what can be improved.
What is checked
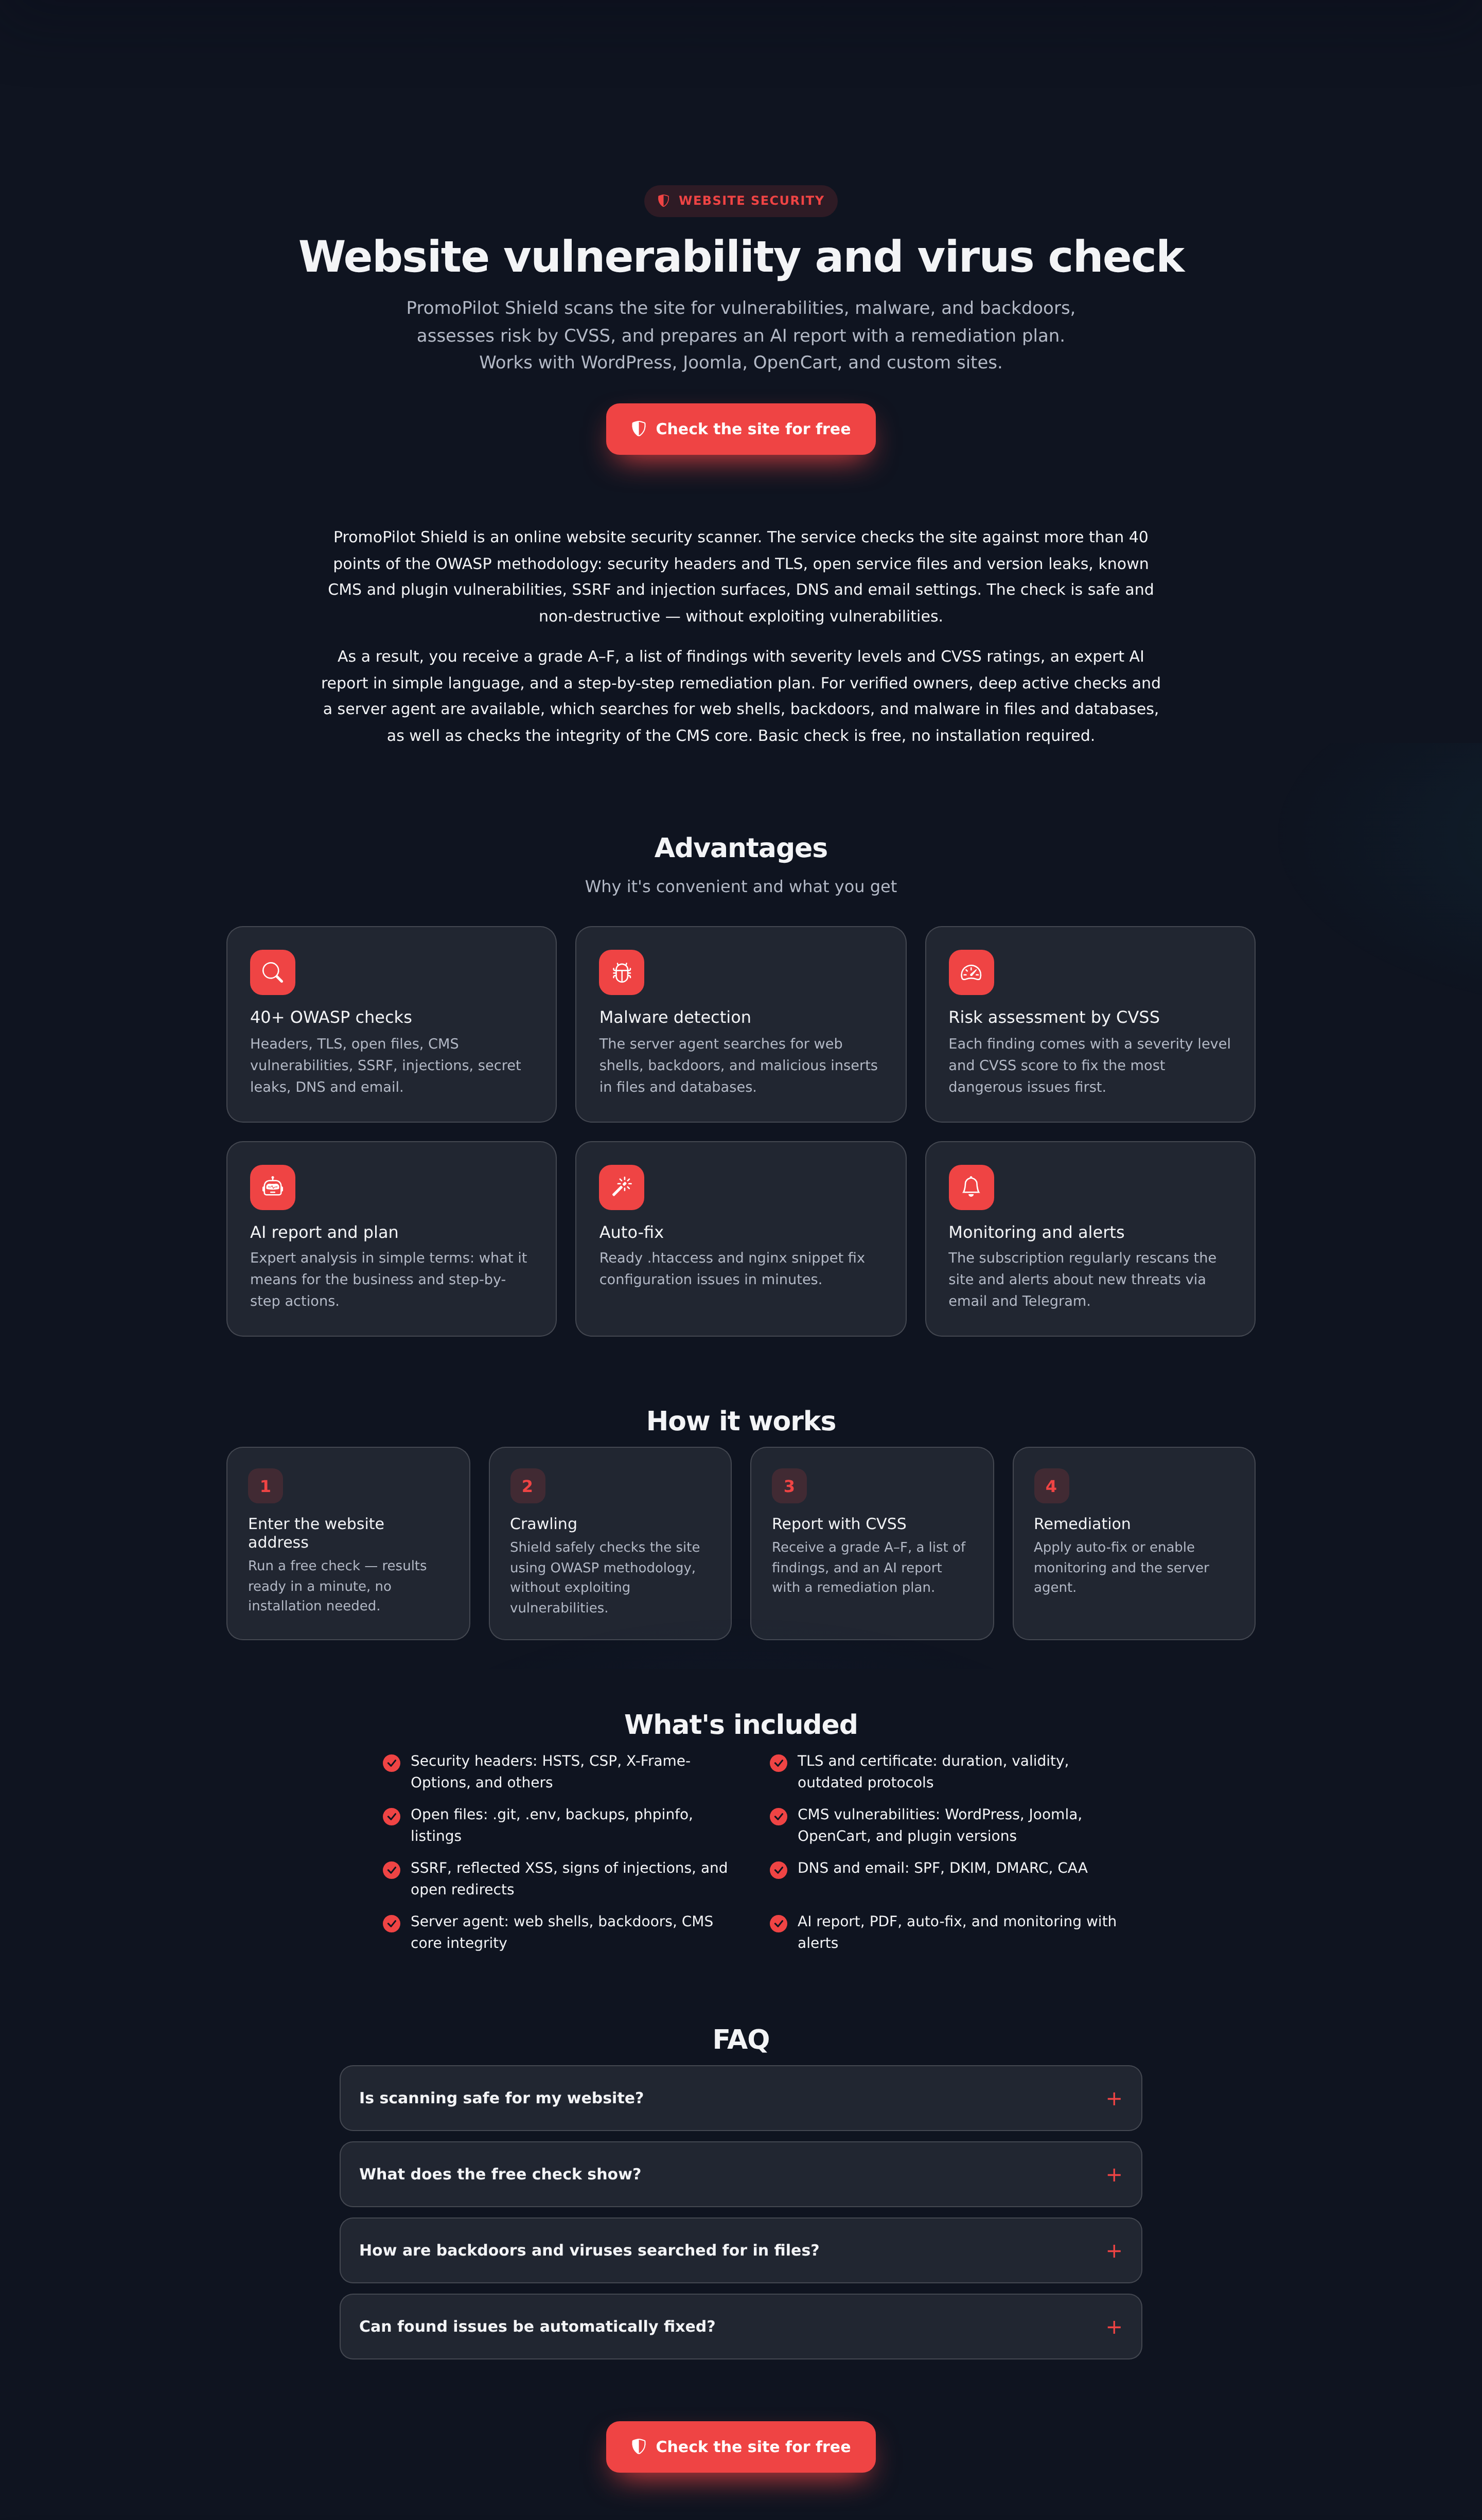
| Direction | What we check |
|---|---|
| Security headers | HSTS, Content-Security-Policy, protection against clickjacking and content type spoofing |
| Encryption | Presence of HTTPS and redirection to it, certificate validity and expiration, outdated TLS versions |
| Data leaks | Open service files and folders, backups, debug pages, software versions in headers |
| Cookies and CORS | Secure, HttpOnly, and SameSite flags, overly broad cross-domain access rules |
| CMS and components | Outdated versions, known vulnerabilities of components, open panels and registration |
| Active probes | Reflected XSS, signs of SQL injections, open redirects |
| Email and DNS | SPF, DMARC, DNSSEC, CAA, risk of subdomain hijacking |
| Malware | Skimmer scripts, miners, hidden frames, spam links, domain blacklisting |
What Shield does not do
This is an external check: it does not replace a full code audit and pentest. There is no separate CSRF check in the scanner — some risks of this class are indirectly reflected in the cookie flag checks.Rating A–F
As a result of the scan, the site receives a letter grade and a list of findings with severity levels. The findings are accompanied by classification according to accepted standards and a clear explanation of the risks and how to fix them.
Domain verification
A quick check is available for any site. Deep scans require verification that the site is yours: through a DNS record, a file in the root, or a meta tag. This protects against using the service to scan other resources.
What to do with the results
- Auto-fix — the service will generate a ready-made server configuration snippet or a list of DNS records for the identified issues.
- Monitoring — subscription to regular checks to learn about problems before visitors do.
- Server agent — an optional script for checking files from the inside, looking for signs of infection.
Analysis of Shield findings
The structure of the report and the two most common groups of findings — open files and signs of hacking.
| Article | About |
|---|---|
| How to read the Shield report | Seventy-nine checks in twelve categories with CVSS rating and links to CWE and OWASP. |
| Shield: file leaks and accesses | The most common category of findings — not viruses, but forgotten files: .env, .git, backups, installers. |
| Shield: malware and backdoors | How infection differs from a backdoor, what traces the scanner looks for, why malware returns after cleaning, and in what order to treat the site. |
FAQ
Does Shield check for CSRF protection?
There is no separate CSRF check in the scanner. Some risks of this class are indirectly reflected in the cookie flag checks.
Why verify the domain?
Deep scans are only possible for your own sites — verification protects against using the service against other resources.
Does this replace a pentest?
No. This is an external automated check; it does not replace code audit and manual penetration testing.
Was this article helpful?
Thank you! We will consider this in future updates.
Try it on your project
Everything described in the article is available in the dashboard — the registration bonus is already in your balance.
Open dashboard